Ethereum Contract Size Limit: What EIP-7954 Changes
EIP-7954 would raise Ethereum runtime code and initcode limits. Learn the 24 KiB to 64 KiB change, deployment impact, trade-offs, and current status.

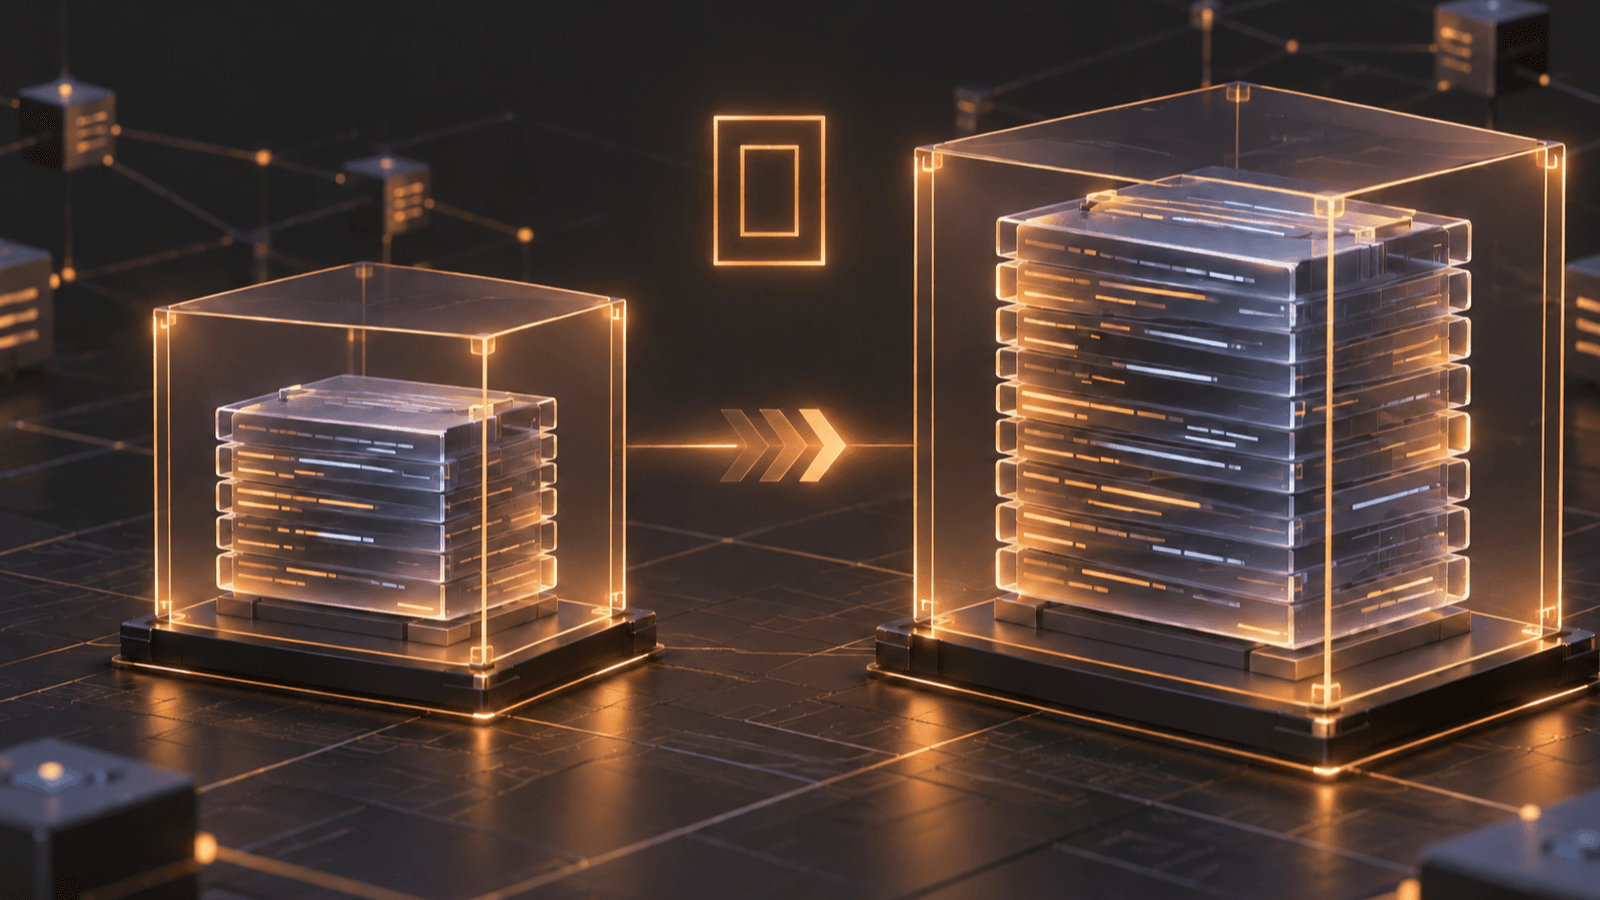
The familiar “contract code size exceeds 24,576 bytes” warning may stop being Ethereum's final boundary—but not yet. Ethereum's contract size limit is scheduled to rise under EIP-7954 as part of Glamsterdam, giving developers more room for runtime code while retaining a hard cap. This guide connects the proposed rule to blockchain and EVM basics and separates what is live today from what still depends on a network upgrade.
As of September 19, 2026, EIP-7954 is in Review. The Glamsterdam meta EIP lists it as Scheduled for Inclusion, but mainnet has no activation timestamp. Ethereum.org says Glamsterdam is testing on devnets, expects mainnet in Q4 2026 without a confirmed date, and identifies October 6 as the next Sepolia fork milestone. Until the relevant fork activates on a network, its existing code-size rules still apply.
What Is Ethereum's Contract Size Limit?
Ethereum limits how many bytes of executable runtime code a newly created contract may store. Under the current EIP-170 rule, contract creation fails if initialization returns more than 0x6000 bytes—24,576 bytes, or 24 KiB.
Think of a contract as a machine that must fit inside a certified enclosure. Source files, comments, tests, and constructor instructions can arrive at the workshop, but the finished machine—the runtime bytecode—must fit inside the enclosure before Ethereum will install it. EIP-7954 proposes a larger enclosure, not an unlimited factory floor.
The cap applies to bytecode, not Solidity source length. Two projects with similar line counts may compile to very different sizes because optimizer settings, libraries, inheritance, revert strings, metadata, and compiler versions affect the output. Measure the exact artifact built for the target chain.
What EIP-7954 Would Change
EIP-7954 changes two consensus constants:
| Object | Current limit | EIP-7954 limit | Increase |
|---|---|---|---|
| Runtime contract code | 24 KiB (0x6000) | 64 KiB (0x10000) | 2.67× |
| Initcode | 48 KiB (0xC000) | 128 KiB (0x20000) | 2.67× |
Runtime code is the executable bytecode stored at the contract address. Initcode is the temporary creation program that runs the constructor and returns that runtime code. The distinction matters because Ethereum checks and charges the two artifacts at different stages.
The proposal preserves the relationship introduced by EIP-3860: the maximum initcode size remains twice the maximum runtime-code size. It does not remove EIP-3860's per-word initcode charge, the code-deposit cost, normal execution gas, or other deployment checks.
The distinction matters at the boundary. Under current rules, returning 24,577 bytes makes contract creation fail. If EIP-7954 activates, a 24,577-byte result could pass this particular size check, while anything above 65,536 bytes would fail it. Passing the size check still does not guarantee deployment: constructor execution can revert, run out of gas, violate another consensus rule, or fail an application-level condition.
Why Ethereum Has a Hard Code Cap
EIP-170 introduced the original limit during Spurious Dragon. Its rationale identifies work that grows with code length: loading code from disk, preprocessing it for EVM execution, and adding code to Merkle proofs. Without a bound, a call priced as constant work could trigger larger node costs.
This resembles an airline raising a baggage allowance. A bigger allowance can remove friction for legitimate passengers, but the aircraft still needs a weight limit. EIP-7954 argues that 64 KiB gives complex applications more flexibility while retaining a conservative bound on block, state, database, and peer-to-peer costs.
The trade-off is real. Larger contracts can carry more features in one address, but they also increase the maximum code a node may need to store, transmit, analyze, and prove. The EIP's security section therefore treats denial-of-service exposure as something constrained—not eliminated—by the new cap.
What Changes for Solidity Developers?
More designs can fit without size-driven splitting
Teams sometimes split logic across libraries, facets, modules, or proxy implementations primarily to stay below 24 KiB. A 64 KiB ceiling gives those teams more design room. It may simplify some deployments and reduce code-size pressure on feature-rich contracts.
That does not make a monolith automatically safer. Smaller components can clarify responsibility and upgrade scope; they can also introduce call boundaries and governance complexity. Larger single contracts can be easier to call but harder to review. Choose architecture from security, maintainability, and trust requirements—not only from the maximum byte count.
Existing contracts do not expand automatically
Already deployed runtime code is immutable at its address. Raising the protocol cap does not append features, relink libraries, or replace an implementation. An upgradeable system still depends on its proxy contract and upgrade authority. A non-upgradeable system needs a new deployment and any application-specific migration.
Deployment can still be expensive
The new ceiling is permission to deploy more code, not a gas discount. More returned runtime bytes generally mean more code-deposit work, and larger creation payloads bring calldata and initcode costs. Glamsterdam also includes separate state-creation and state-access repricing proposals, so teams should test the complete fork rules rather than extrapolate today's receipt. See the Glamsterdam gas repricing guide for that neighboring change.
Tooling must know the target fork
A compiler or deployment tool may warn at the old threshold even when a test network has activated the new rules, or a local development chain may accept a large contract that the target network still rejects. Record the chain ID, block or fork configuration, client version, compiler version, optimizer settings, and measured byte lengths with every test result.
Practical Migration and Testing Checklist
- Measure both artifacts. Record complete initcode and returned runtime code in bytes, not hexadecimal characters.
- Test against today's limit first. If a deployment must work before Glamsterdam activation, keep runtime code at or below 24 KiB and initcode at or below 48 KiB.
- Pin the fork configuration. Do not label a local VM run “Glamsterdam-ready” unless its rules match the intended client release and network milestone.
- Exercise boundary cases. Test exactly at and one byte above 24 KiB, 64 KiB, 48 KiB, and 128 KiB where applicable.
- Re-estimate gas. Include transaction data, initcode metering, constructor execution, storage creation, and code deposit—not just runtime byte count.
- Re-run security analysis. Larger code can expand the audit surface, control flow, and number of privileged branches even if deployment succeeds.
- Retest CREATE and CREATE2 factories. Factory assumptions, salts, initcode hashes, and nested creation paths can change when artifacts change.
- Keep a smaller fallback. Until mainnet activation and production client support are confirmed, retain a deployable architecture that respects the live cap.
Risks and Limitations
- Activation risk: EIP-7954 is scheduled but not active on mainnet as of September 19, 2026. The specification or schedule can change before activation.
- Cross-chain mismatch: EVM-compatible networks choose their own forks and limits. Acceptance on one chain does not prove acceptance on another.
- Resource trade-offs: a larger maximum increases worst-case code storage, propagation, preprocessing, and proof-related work for nodes.
- Audit complexity: fitting more code into one address can enlarge the review surface and make rarely used branches easier to miss.
- Deployment-cost risk: a larger allowance does not make large deployments cheap or ensure a transaction fits other gas constraints.
- Architecture risk: using the extra room to avoid all modularity can create tightly coupled systems that are difficult to test or replace.
- Market risk: a protocol feature does not predict ETH's price. Crypto assets are volatile; use only funds you can afford to lose and do your own research.
Frequently Asked Questions
Is Ethereum's contract size limit already 64 KiB?
No on mainnet as of September 19, 2026. EIP-7954 is in Review and scheduled for Glamsterdam, while mainnet has no activation timestamp. The current EIP-170 limit remains 24 KiB until activation.
Does EIP-7954 remove the initcode limit?
No. It proposes raising the initcode limit from 48 KiB to 128 KiB. EIP-3860's distinction between initcode and stored runtime code remains important.
Will every 60 KiB contract deploy after activation?
Not necessarily. It may pass the new runtime-size check, but deployment can still fail because of initcode size, insufficient gas, constructor reverts, state-creation costs, or other consensus and application rules.
Does a proxy bypass the code-size limit?
Each deployed contract is checked separately, so a proxy system can distribute logic across addresses. That is not a free bypass: delegate calls, storage layout, upgrade keys, and governance add distinct security risks.
Should developers stop optimizing bytecode size?
No. Smaller code can reduce deployment cost and audit surface. The higher cap provides headroom; it does not turn code size into a meaningless metric.
Primary Sources
- EIP-7954: Increase Maximum Contract Size
- EIP-170: Contract Code Size Limit
- EIP-3860: Limit and Meter Initcode
- EIP-7773: Glamsterdam Hard-Fork Meta
- Ethereum.org: Glamsterdam Roadmap
- Ethereum execution-spec test releases
Bottom Line
EIP-7954 would move Ethereum's runtime-code ceiling from 24 KiB to 64 KiB and its initcode ceiling from 48 KiB to 128 KiB. That creates useful headroom for complex applications while keeping explicit bounds on node work. It does not erase deployment gas, architecture choices, audits, or network-specific activation checks.
Treat the 64 KiB figure as a scheduled Glamsterdam rule until the target network activates it. Verify the current EIP, client release, and fork configuration before deploying. This article is educational, not financial advice; smart-contract actions can be irreversible, crypto assets are volatile, and you should do your own research (DYOR/NFA).
Keep learning
Ethereum Initcode vs Runtime Bytecode: What Actually Gets Deployed
Learn how Ethereum initcode runs once, returns runtime bytecode, and affects constructor arguments, gas, size limits, verification, and CREATE2.
 GOMTU9 min read
What Are Smart Contracts? How They Work and Real Use Cases
Discover what smart contracts are, how they work on the blockchain, and their real-world use cases in DeFi, NFTs, and RWA — plus risks, limits, and FAQ.
GOMTU7 min readEthereum Proxy Contracts Explained: Delegatecall, UUPS, and Upgrade Risks
Learn how Ethereum proxy contracts use delegatecall, how transparent, UUPS, and beacon proxies differ, and how to verify upgrade authority safely.
GOMTU9 min readExplore related topics

Ethereum Glamsterdam Upgrade: ePBS, BALs, and What Is Actually Planned
Ethereum Glamsterdam is expected in Q4 2026. Learn its frozen scope, Sepolia milestone, ePBS, block-level access lists, and remaining uncertainties.
GOMTU7 min readCrypto Address Poisoning: How to Verify Wallet Addresses Before You Send
Crypto address poisoning plants a lookalike address in your transaction history. Learn how it works and follow a safer verification checklist.
GOMTU7 min read