Ethereum Weak Subjectivity: Why New Nodes Need a Trusted Checkpoint
Learn how Ethereum weak subjectivity checkpoints stop long-range attacks, how checkpoint sync works, and what node operators must verify.

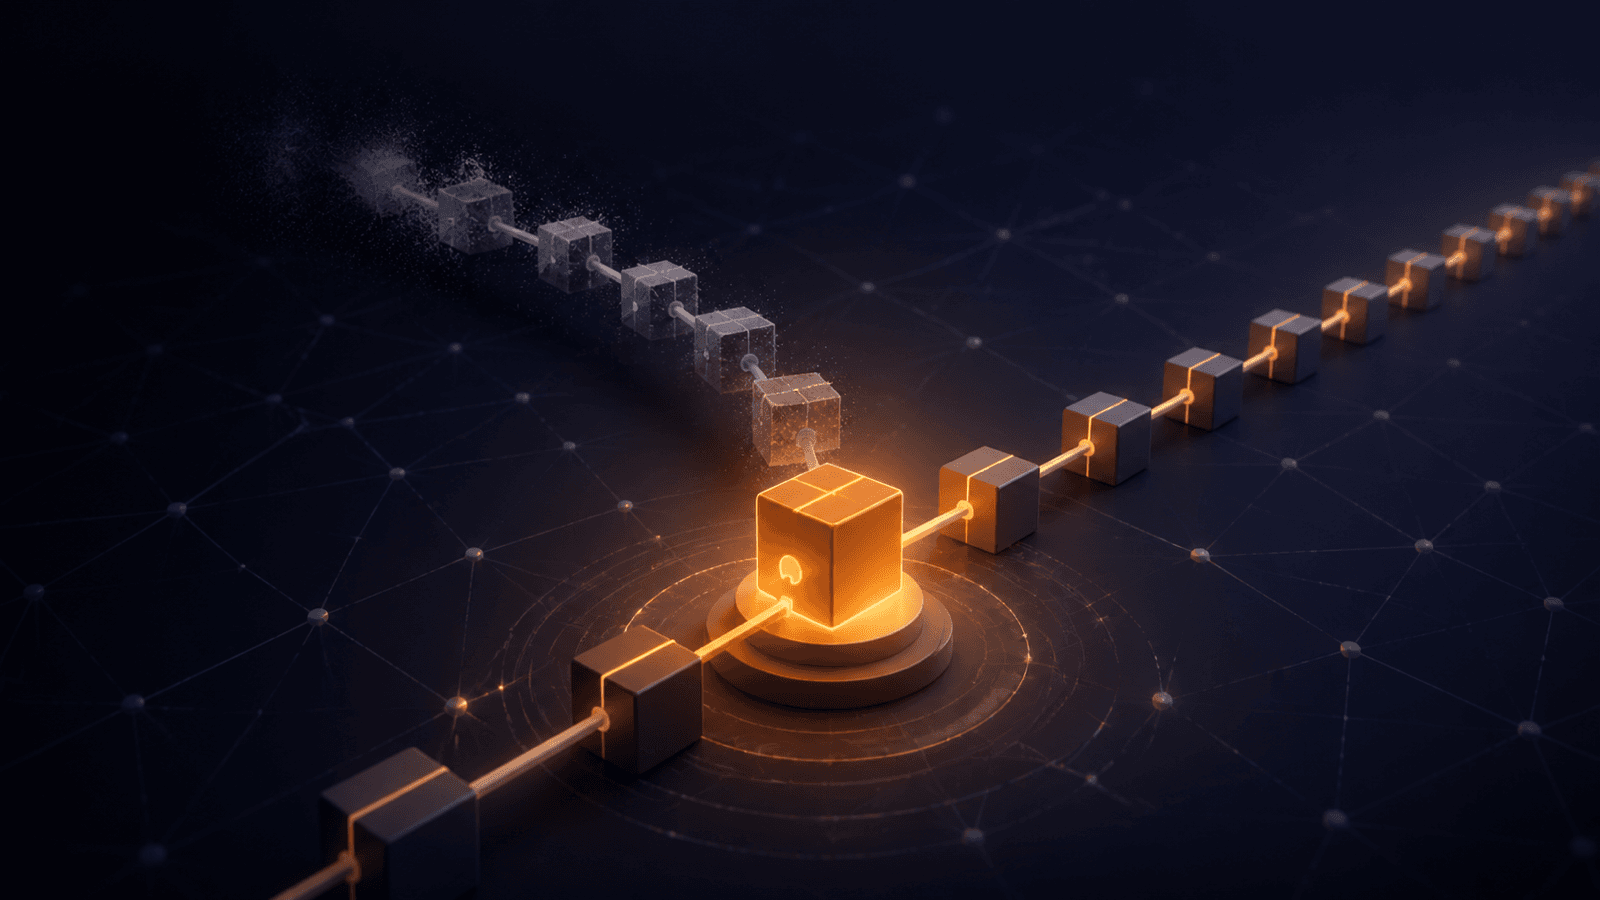
Imagine restarting an Ethereum node after it has been offline for years. Its software can verify signatures and protocol rules, but two internally valid histories may be presented to it. Which history represents the network everyone else recognizes? Blockchain infrastructure cannot answer that question from old protocol data alone.
This is the problem Ethereum weak subjectivity addresses. A new or long-offline proof-of-stake node begins from a recent checkpoint obtained through a trusted channel, then verifies the chain objectively from that anchor onward. It is a narrow trust assumption, not permission to trust every future block or RPC response.
What Weak Subjectivity Means
In an objective system, applying the protocol rules to available histories is enough to select one chain. A subjective system depends on social information. Weak subjectivity sits between them: you need a small piece of recent social information at startup, after which normal verification rules take over.
Think of the checkpoint as a meeting point printed on a trusted invitation. Once everyone starts from that verified location, they can follow the route signs themselves. The invitation does not drive the car or approve every turn. It prevents someone from handing a late arrival a convincing map that begins in the wrong city.
On Ethereum, a weak subjectivity checkpoint is a recent state root or checkpoint that the operator accepts as belonging to the canonical chain. The node rejects histories that conflict with it and processes blocks forward according to consensus rules.
Why Proof of Stake Needs It
Proof-of-stake chain selection relies on validator votes. Validators can eventually exit and withdraw their stake. After withdrawal, the protocol can no longer slash that old stake, even if former validators use historical keys to sign an alternative history.
That creates the basis for a long-range attack. An attacker may construct an old fork using keys that were valid at the time and release it much later. A node that stayed online has already followed recent finality. A new node needs a way to distinguish the socially accepted chain from a fabricated but structurally plausible history.
The checkpoint supplies that boundary. Ethereum.org describes it as a revert limit: history before the accepted checkpoint cannot be replaced from the node's perspective. Keeping the checkpoint recent relative to protocol withdrawal and safety conditions prevents withdrawn validators from rewriting the remote past for newcomers.
This differs from short reorganizations near the head. Fork choice handles competing recent blocks using accumulated attestations. Weak subjectivity answers the bootstrap question: which finalized history should the node treat as its starting truth?
How Checkpoint Sync Works
Ethereum clients commonly use checkpoint sync, also called weak subjectivity sync, to start a consensus node without replaying the Beacon Chain from genesis.
- Obtain a recent checkpoint or finalized state. Select a source and record the expected checkpoint.
- Cross-check the anchor. Compare independent sources such as client documentation, reputable explorers, public endpoints, or a known node operator.
- Initialize the consensus client. The client accepts the checkpoint as its anchor and downloads recent state or block data.
- Verify forward. It checks signatures, state transitions, fork choice, and later finality as normal.
- Backfill when supported. Historical blocks may be downloaded, but must form a valid chain to the trusted state and carry valid proposer signatures.
Checkpoint sync can sharply reduce initial synchronization time. Go Ethereum's current documentation says a consensus client can sync in minutes this way, though exact behavior and flags belong to the chosen consensus client.
The anchor does not make a partly synced validator ready to sign. Ethereum's consensus specifications state that an optimistic node must not propose, attest, or join sync committees while it cannot fully validate relevant execution data. Wait for both consensus and execution clients to report a healthy, non-optimistic state.
Checkpoints vs Finalized Blocks
A finalized block has received the protocol's required validator votes. Reverting it requires a critical consensus failure and substantial slashing. Our blockchain finality guide explains that economic guarantee.
A weak subjectivity checkpoint plays another role. The operator supplies it out of band, and the node treats conflicting history as invalid. If a node learns of two conflicting finalized checkpoints without an accepted anchor, code alone may not identify the community-recognized chain. The trusted checkpoint resolves that rare bootstrap ambiguity.
| Signal | How it is obtained | What it does |
|---|---|---|
| Finalized block | On-chain validator votes | Gives economic settlement within the followed chain |
| Weak subjectivity checkpoint | Recent trusted source | Selects the canonical history from which a node starts |
| Chain head | Fork choice and recent attestations | Selects the latest tip, which may not be finalized |
A Safer Operator Checklist
- Use current client documentation. Flags and supported modes change.
- Cross-check independent sources. Two pages backed by one provider are not independent.
- Confirm network identity. A testnet checkpoint is not a Mainnet anchor.
- Prefer a recent finalized checkpoint. Do not reuse an old value merely because it once worked.
- Verify status before validating. Do not sign while either client is syncing or execution remains optimistic.
- Protect the source path. A compromised site, DNS path, or chat account can supply a malicious value.
- Keep client diversity in mind. Independent implementations reduce dependence on one software team.
Light clients face a related bootstrap problem. They maintain a compact verified view rather than a full database, but still need a trustworthy starting point. See our Ethereum light client guide for the difference between authenticating headers and verifying an RPC claim.
Risks and Limitations
A poisoned checkpoint is a poisoned foundation. Verification after a malicious anchor can consistently validate the wrong branch. Cross-checking matters most at bootstrap.
Trust is reduced, not eliminated. You still trust some combination of providers, client binaries, operating systems, hardware, and configuration. Multiple sources lower correlated risk without creating mathematical certainty.
Stale checkpoints weaken safety. Acceptable age depends on protocol state and client calculations. Avoid treating one number of days as permanent; use current client guidance.
Sync status can be misunderstood. A node may know the consensus head while execution validation is still catching up. Signing during an optimistic state creates validator risk.
Weak subjectivity does not secure applications. It does not audit contracts, protect keys, guarantee RPC availability, or make ETH prices predictable. It solves a specific history-selection problem.
FAQ
Does Ethereum trust one central checkpoint server?
No universal server is appointed. Operators can compare checkpoints from public endpoints, explorers, client teams, or node operators instead of trusting one channel blindly.
Must every Ethereum user manage a checkpoint?
Usually not. This is primarily a node-bootstrap concern. Wallet and hosted-RPC users inherit their providers' infrastructure choices.
Is checkpoint sync the same as snap sync?
No. Checkpoint sync anchors the consensus layer. Execution-layer snap sync is a different technique for acquiring and verifying execution state.
How recent should the checkpoint be?
There is no timeless calendar answer. The weak subjectivity period depends on protocol parameters and validator conditions. Follow current consensus-client documentation.
Primary Sources
Sources accessed August 19, 2026:
- Ethereum.org: Weak Subjectivity
- Ethereum.org: Nodes and Clients
- Ethereum Consensus Specifications: Optimistic Sync
- Ethereum Consensus Specifications: Phase 0 P2P Interface
- Go Ethereum: Sync Modes
Weak subjectivity is a deliberately bounded trust assumption: verify a recent starting point, then let protocol rules verify the path ahead. This is educational, not financial advice (NFA). Crypto assets remain volatile; use only funds you can afford to lose and do your own research (DYOR).
Keep learning
Blockchain Finality Explained: When Is a Crypto Transaction Really Settled?
Learn how blockchain finality differs from confirmation, why Bitcoin and Ethereum settle differently, and what to check before moving funds again.
 GOMTU7 min read
Ethereum Light Clients and Trustless RPC: Verify Without a Full Node
How Ethereum light clients verify headers and RPC data, what trustless RPC can prove, and which security and privacy limits remain.
GOMTU5 min read
Consensus Algorithms Explained: PoW vs PoS vs DPoS
Learn how blockchain consensus algorithms work — from Proof of Work to Proof of Stake, DPoS, BFT, and PoH. Compare trade-offs, real-world use cases, risks, and what it all means for your gas fees and staking activity.
GOMTU9 min readExplore related topics
Crypto Address Poisoning: How to Verify Wallet Addresses Before You Send
Crypto address poisoning plants a lookalike address in your transaction history. Learn how it works and follow a safer verification checklist.
GOMTU7 min read
Cross-Chain Bridge Guide: How to Bridge Safely in 2026 (Step-by-Step)
Learn how to use cross-chain bridges safely: what they are, how lock-and-mint and liquidity pool bridges work, a step-by-step tutorial, and how to avoid the hacks that cost DeFi over $2.8B.
GOMTU9 min read