Merkle Trees and Merkle Proofs Explained: Verify Data Without the Whole Blockchain
Learn how Merkle trees compress many transactions into one root hash, how inclusion proofs work, and where Bitcoin, Ethereum, and rollups use them.

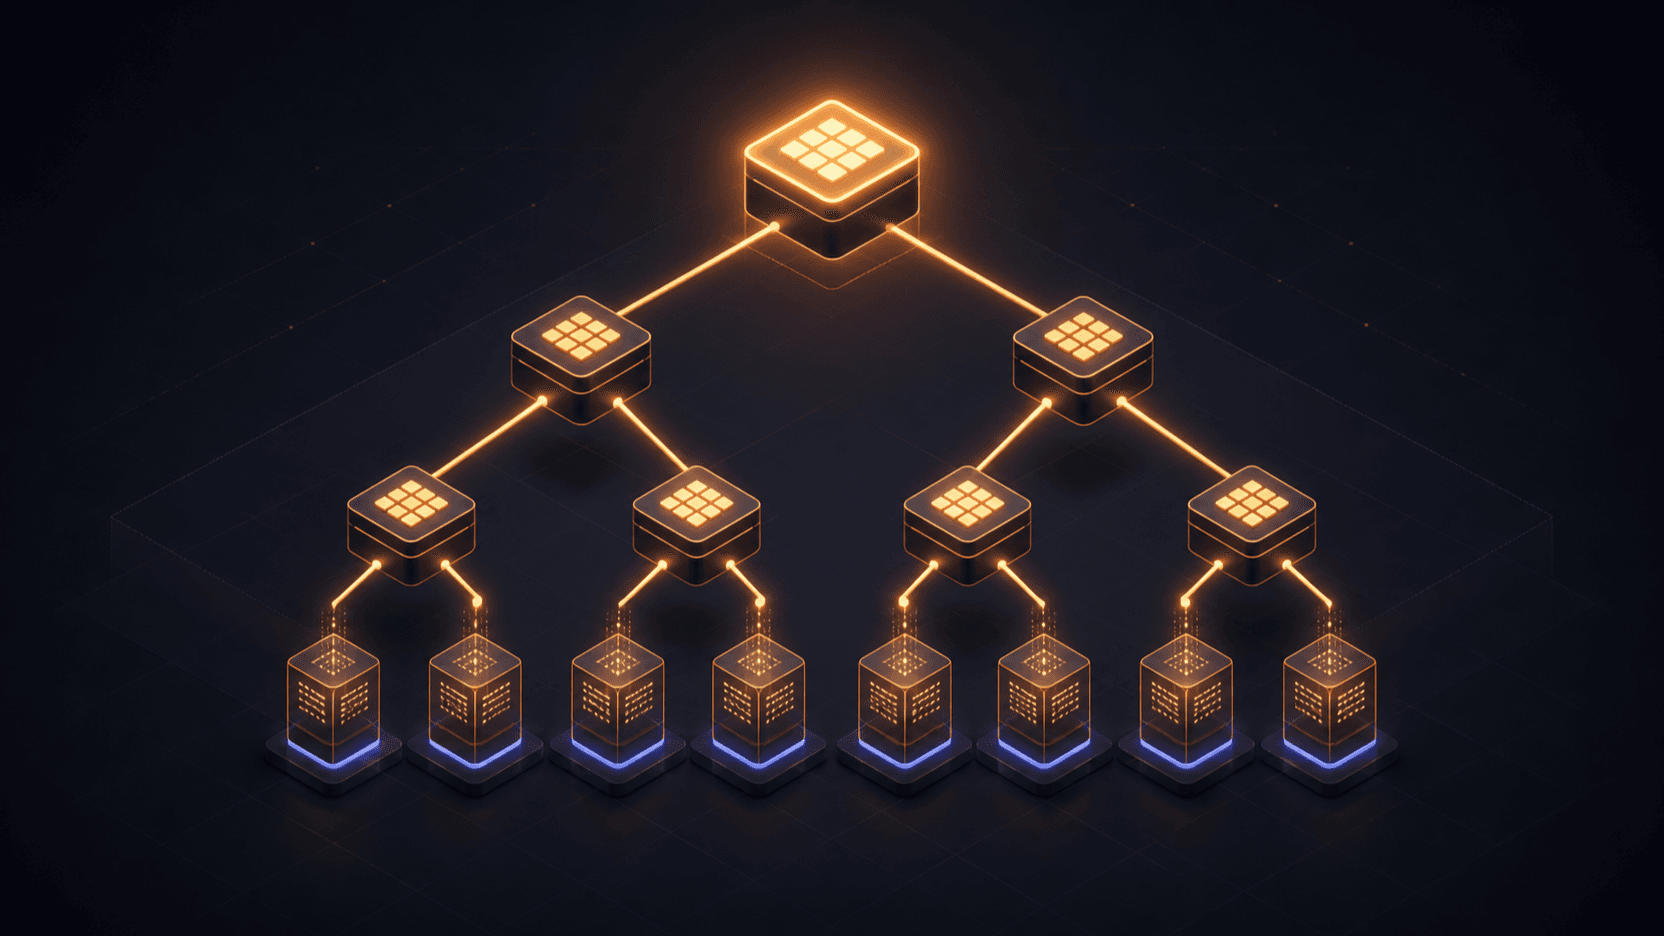
A blockchain may contain millions of records, yet a lightweight wallet can check one transaction without downloading and trusting every byte. The trick is not a smaller copy of the ledger. It is a compact trail of hashes called a Merkle proof.
This idea sits underneath many blockchain basics, from Bitcoin block headers to Ethereum state and rollup proofs. It is powerful, but narrow: a valid Merkle proof establishes a relationship to a particular root. It does not prove that the root is canonical, the transaction is economically final, or the application is safe.
What Is a Merkle Tree?
A Merkle tree is a hierarchy of hashes. Data items sit at the leaves. Pairs of leaf hashes are combined and hashed again, then those parent hashes are paired and hashed until one value remains: the Merkle root.
Think of a warehouse sealing process. Each box receives a tamper-evident seal, pairs of boxes receive a larger seal, and the whole shipment receives one final seal. You can inspect one box by checking only the seals along its route to the shipment seal. You do not need to reopen every other box.
For a simple four-leaf tree:
                 Root = H(AB || CD)
                  /              \
          AB = H(A || B)      CD = H(C || D)
             /      \            /      \
          H(A)      H(B)       H(C)      H(D)
H() means a cryptographic hash function and || means concatenation. Real protocols define exact serialization, byte order, hashing, and odd-leaf rules. Those details are consensus-critical; implementations cannot freely substitute the diagram's simplified recipe.
How a Merkle Proof Works
Suppose you want to prove that item C belongs to the tree. You provide C plus the neighboring hashes needed to reconstruct the root:
- Hash C.
- Combine it with sibling
H(D)to reconstructCD. - Combine
CDwith siblingABto reconstruct the root. - Compare the result with the trusted root.
If the calculated and trusted roots match, the verifier has an inclusion proof for C under that root. Changing C changes its leaf hash, which changes every parent on the path and ultimately changes the root.
The proof stays small because it includes one sibling hash per tree level, not every leaf. For a balanced tree, the path grows logarithmically: doubling the number of leaves adds roughly one proof element. This is why Merkle structures are useful when a verifier has limited bandwidth, storage, or on-chain computation.
An exclusion proof tries to show that an item is absent. That is not automatically available from every plain binary Merkle tree. Ordered trees, sparse Merkle trees, and authenticated tries define additional structure that can support non-membership proofs. Always check the exact construction before assuming “not found” is cryptographically proven.
What the Root Proves—and What It Does Not
A Merkle root is a compact commitment to data arranged under a protocol's rules. Given a correct proof and the expected root, a verifier can check membership without receiving the full dataset.
The expected root is the crucial trust anchor. A proof against a root copied from an attacker's website can be mathematically valid and operationally useless. A wallet or light client must connect the root to a block header, consensus state, finalized checkpoint, or another source it has reason to trust.
Merkle proofs also do not establish:
- that a transaction is valid under every protocol rule;
- that its block belongs to the canonical chain;
- that the block has enough confirmations or finality;
- that a smart contract has no bug;
- that an asset or protocol is a sound investment.
Our blockchain finality guide covers the separate question of when chain history is sufficiently difficult to reverse.
How Bitcoin Uses Merkle Trees
Bitcoin commits to a block's transactions through the Merkle root stored in the block header. Bitcoin's developer reference specifies that transaction IDs are ordered according to consensus rules, paired, concatenated, and double-SHA-256 hashed through intermediate rows. A block with only its coinbase transaction uses that transaction ID as the root.
This design lets a verifier check that a transaction was included in a particular block using the transaction's branch rather than every transaction in that block. The verifier still needs a trustworthy block header and a way to evaluate the chain of headers. Inclusion in a candidate block is not the same as adequate confirmation.
How Ethereum Uses Authenticated Tries
Ethereum's execution layer uses a modified Merkle-Patricia Trie (MPT) for authenticated key-value data. The Ethereum.org documentation describes it as deterministic and cryptographically verifiable: identical state produces the same root, while changing underlying values changes the path hashes and root.
This is more than a binary list of transactions. A trie follows key paths, and Patricia compression shortens stretches with no branching. Ethereum block headers commit to roots associated with state, transactions, and receipts. Applications can request account and storage proofs, though the exact RPC format and client behavior matter.
Ethereum's consensus layer also uses SSZ merkleization for structured data. The shared principle is a small root commitment plus a branch that lets a verifier recompute it; the data layout and hashing rules differ.
Merkle Proofs in Rollups and Smart Contracts
Merkle proofs appear wherever one system needs to verify a small claim about a larger dataset:
- Rollups: Ethereum's ZK-rollup documentation describes transaction and account membership branches among the inputs used to prove state transitions.
- Airdrop claims: a contract can store one root and verify that a claimant's address and allocation appear in an off-chain list.
- Bridges and light clients: a destination system can verify that a message or receipt belongs to an authenticated source structure, alongside separate consensus assumptions.
- Allow-lists: applications can verify membership without writing every eligible address into contract storage.
Smart-contract developers must define leaf encoding exactly. Ambiguous concatenation, missing domain separation, duplicate leaves, incorrect pair ordering, or a compromised root publisher can break the intended security even when the hash function itself remains sound. Learn the broader execution risks in what smart contracts are.
Risks and Common Misunderstandings
- Trusting the wrong root: verification only anchors to the supplied root. Authenticate where that root came from.
- Confusing inclusion with finality: a branch can match a block that later loses the fork-choice race.
- Ignoring encoding rules: the same human-readable values can hash differently when serialized differently.
- Assuming all trees prove absence: non-membership depends on the data structure and proof scheme.
- Reusing proofs after state changes: a proof normally targets a specific root and may become stale when the dataset changes.
- Treating cryptography as application safety: valid membership says nothing about key theft, contract logic, governance, custody, or market volatility.
For financial applications, verify the root source, contract address, proof-generation code, and current protocol documentation. Test with low-value interactions where practical. Crypto assets and protocols can fail or lose value; use only funds you can afford to lose and do your own research (DYOR).
FAQ
Is a Merkle root the hash of all blockchain data?
Not necessarily. A root commits to the dataset and structure defined by a particular protocol. Bitcoin's block Merkle root covers that block's transactions, while Ethereum uses multiple authenticated structures and roots for different data.
Can someone fake a Merkle proof?
A verifier should reject a branch that does not reconstruct the expected root. Security still depends on the hash construction, correct implementation, unambiguous encoding, and an authentic expected root.
Does a Merkle proof reveal the whole dataset?
No. A typical inclusion branch reveals the target data or leaf hash and sibling hashes along one path. Application-specific metadata may still leak, so “compact” does not automatically mean “private.”
Are Merkle proofs the same as zero-knowledge proofs?
No. A standard Merkle proof reveals a hash path and proves membership relative to a root. A zero-knowledge proof can establish a broader statement while hiding witness data. Some ZK systems use Merkle paths inside their circuits.
Primary Sources
Sources accessed August 16, 2026:
- Bitcoin Developer Reference: Merkle Trees
- Ethereum.org: Merkle Patricia Trie
- Ethereum.org: Data Structures and Encoding
- Ethereum.org: Zero-Knowledge Rollups
Merkle trees turn a large dataset into a compact commitment, and Merkle proofs let you verify one path back to that commitment. Keep the boundary clear: verify the root's origin, then evaluate consensus, finality, application logic, and financial risk separately. This article is educational and not financial advice (NFA).
Keep learning
Blockchain Finality Explained: When Is a Crypto Transaction Really Settled?
Learn how blockchain finality differs from confirmation, why Bitcoin and Ethereum settle differently, and what to check before moving funds again.
 GOMTU7 min read
Zero-Knowledge Proofs Explained: zk-SNARKs, zk-STARKs & ZK Rollups
Zero-knowledge proofs let you prove something is true without revealing the data. Learn how zk-SNARKs, zk-STARKs, and ZK rollups power privacy and Ethereum scaling.
GOMTU8 min read
What Are Smart Contracts? How They Work and Real Use Cases
Discover what smart contracts are, how they work on the blockchain, and their real-world use cases in DeFi, NFTs, and RWA — plus risks, limits, and FAQ.
GOMTU7 min readExplore related topics
Crypto Address Poisoning: How to Verify Wallet Addresses Before You Send
Crypto address poisoning plants a lookalike address in your transaction history. Learn how it works and follow a safer verification checklist.
GOMTU7 min read
Bitcoin Hits 20 Million Coins Mined: What the Scarcity Milestone Tells Us
On March 9, 2026, Bitcoin mined its 20 millionth coin — 95.2% of all supply is now in circulation. A look at the supply architecture, halving schedule, and observable patterns from past cycles. Not financial advice.
GOMTU8 min read