ERC-7579 Modular Smart Accounts: Validators, Executors, Hooks, and Risks
Learn how draft ERC-7579 standardizes modular smart accounts, what its four module types do, and which installation risks users and builders must check.
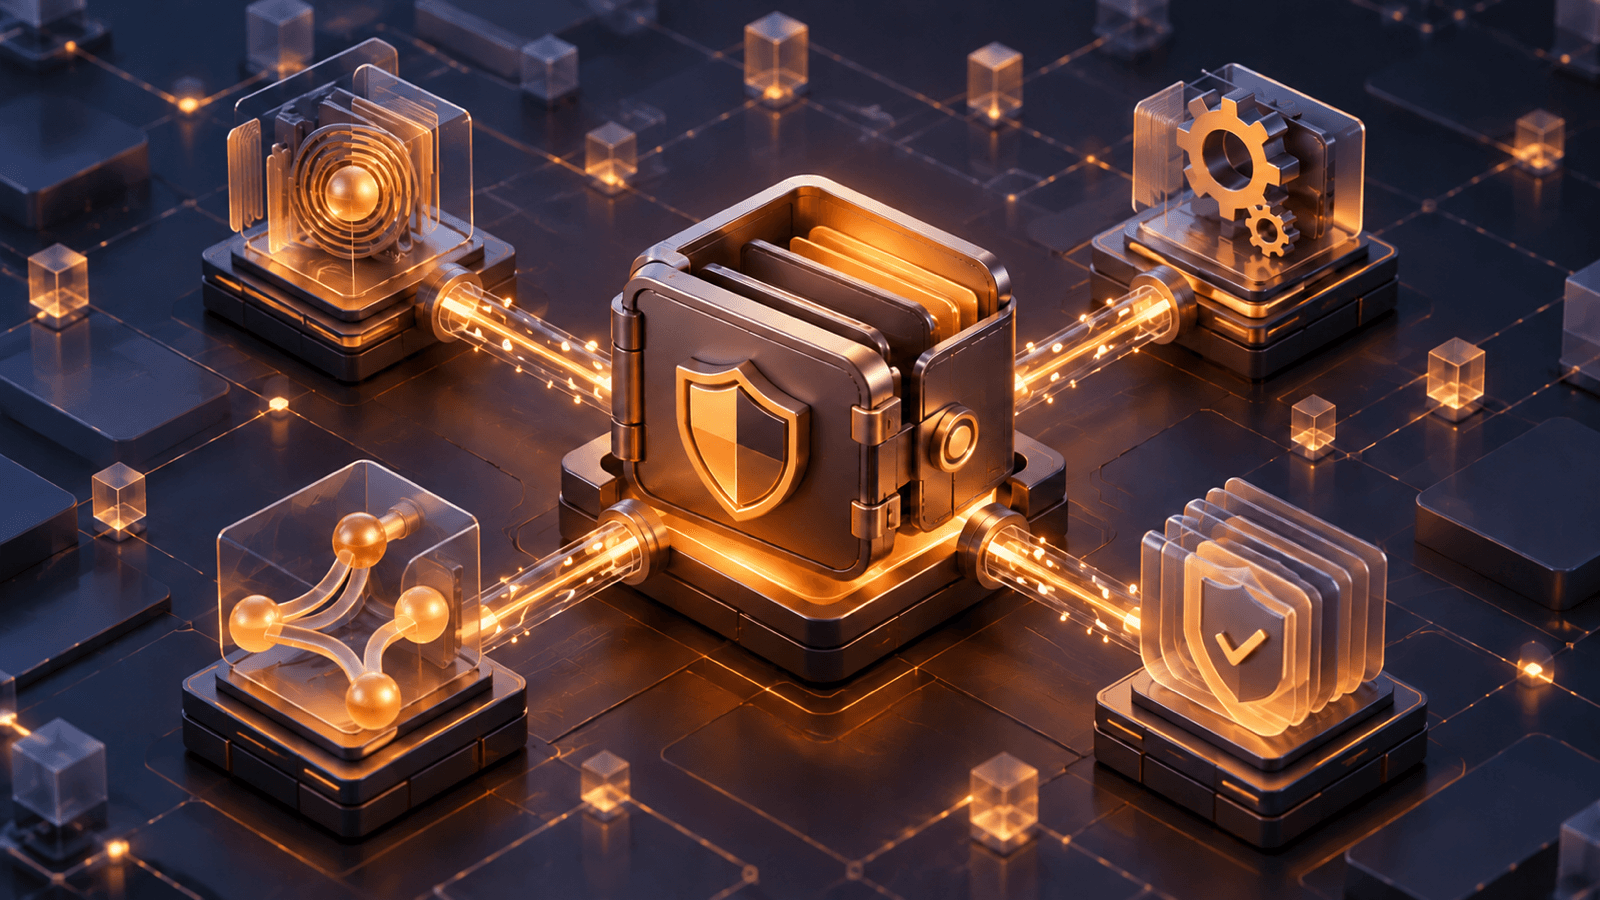
A smart wallet can support recovery, automation, and alternative signatures—but adding every feature directly to one account makes upgrades and integrations brittle. ERC-7579 modular smart accounts take a plug-in approach inside the broader crypto wallet security landscape. The draft standard defines a small common interface for accounts and modules, while leaving wallet teams free to design the machinery behind it.
Important
As of October 25, 2026, the official ERC page marks ERC-7579 as Draft. It is not a protocol upgrade that every Ethereum wallet automatically supports. Compatibility depends on the specific account implementation, adapter, module, network, and software version.
What ERC-7579 Is Trying to Standardize
Smart accounts are programmable contract accounts. Their rules can support multisignatures, passkeys, recovery guardians, spending policies, scheduled actions, and other features that a single-key externally owned account cannot express by itself. If that distinction is new, start with the account abstraction and smart wallets guide.
The problem is fragmentation. One wallet may expose recovery as a proprietary module, while another expects different installation calls, execution formats, and validation behavior. A developer then has to rebuild the same feature for each account system, and users can become locked into one vendor's module ecosystem.
The official ERC-7579 specification defines minimum interfaces and behavior intended to make modules portable across compliant smart accounts. It covers execution, account configuration, module installation, ERC-1271 signature handling, and optional fallback and hook behavior. It deliberately does not prescribe one internal account architecture.
Think of it like USB for smart-wallet features. USB specifies how compatible devices connect and communicate; it does not dictate the circuitry inside every keyboard or laptop. Likewise, ERC-7579 gives accounts and modules a shared socket without claiming that every plug-in is safe or that every compliant wallet behaves identically.
The Four ERC-7579 Module Types
The draft separates modules by authority. That separation matters because checking a signature is not the same power as initiating a transaction.
| Module type | Type ID | Main job | Example use | Main security question |
|---|---|---|---|---|
| Validator | 1 | Decides whether an operation or signature is valid | Passkey, multisig, or recovery validation | Can it approve an unauthorized operation? |
| Executor | 2 | Calls the account to execute actions | Scheduled payment or automated strategy | Who can trigger it, and what can it call? |
| Fallback handler | 3 | Extends how the account responds to function calls | Add an interface the base account lacks | Is the original caller preserved and checked? |
| Hook | 4 | Runs checks before and/or after execution | Spending policy or compliance check | Can it block the account or miss a dangerous path? |
A single contract may identify as more than one module type. The account must still track module types distinctly so authorization intended for an executor is not accidentally granted to a validator. The specification calls out this distinction as a security boundary.
Validators decide whether authority is valid
A validator handles the account's authorization logic. Under the current ERC-4337-dependent design, it validates a packed UserOperation and may also support ERC-1271 contract-signature checks. That could enable a passkey validator, a threshold-signature validator, or a recovery rule.
ERC-7579 standardizes the interface, not the trustworthiness of the rule. A validator with a bug or malicious upgrade path could accept operations the owner never intended. For the underlying signature model, see ERC-1271 smart contract signatures.
Executors can act on behalf of the account
An executor can call executeFromExecutor after it is installed and authorized. This supports useful automation, but it is powerful: the executor may initiate calls without asking the owner for a fresh signature each time, depending on its own rules.
Treat an executor like an employee with a corporate card. The job may require spending authority, but the useful question is not simply “Do I trust this employee?” It is “Which merchants, amounts, and dates can this card use?” Module installation should be paired with narrow scope, clear triggering conditions, and a tested removal path.
Fallback handlers extend account behavior
A fallback handler can respond to functions the base account does not implement. ERC-7579 says compliant forwarding must use call or staticcall, append the original caller using ERC-2771 semantics, and route by function selector. Incorrect caller handling can turn a compatibility feature into an authorization flaw.
Hooks check execution context
Hooks are optional. They can run preCheck before an execution and postCheck afterward. A hook might enforce a spending ceiling or inspect an outcome, but it also becomes part of the critical path. A malicious or broken hook can revert and deny access to the account.
How Installation and Execution Work
At a high level, a compliant flow looks like this:
- The app inspects the account.
accountId,supportsModule, andsupportsExecutionModeexpose the implementation identity and supported capabilities. - The owner authorizes installation. The account calls
installModulewith a module type, address, and initialization data. - The account records the module by type. It calls the module's
onInstallfunction and emitsModuleInstalledif setup succeeds. - The module performs its limited role. A validator checks authority, an executor requests a call, a fallback handler extends an interface, or a hook checks context.
- The account enforces execution rules. Unsupported modes must revert, and execution entry points need appropriate authorization.
- The owner can uninstall the module. The account calls
onUninstall, removes the registration, and emitsModuleUninstalled—assuming the module does not maliciously block removal.
Execution uses a 32-byte mode that describes call type, failure behavior, and space for extensions. Accounts can advertise support for single calls, batches, static calls, or delegatecalls rather than pretending every implementation supports every mode.
ERC-7579 currently depends on ERC-4337 for its validation flow. That means bundlers, the EntryPoint, and UserOperations remain relevant. The standard's authors describe a possible future path that moves this dependency into an extension if other account-abstraction architectures need the interface. Gas sponsorship is a separate concern; the ERC-4337 paymasters guide explains who pays and why a sponsored operation can still fail.
What Interoperability Does—and Does Not—Guarantee
Safe's ERC-7579 documentation describes the goal as allowing modules to work across supporting account implementations. Safe itself uses a Safe7579 Adapter to expose the required behavior rather than replacing its entire account design.
That illustrates the standard's minimal approach. Compliance can reduce custom integration work and vendor lock-in, but it does not guarantee:
- that every account supports every execution mode or optional hook;
- that identical modules have identical configuration across wallets;
- that a module has been audited or is safe for valuable assets;
- that an adapter preserves every security assumption of the underlying account; or
- that a draft interface will remain unchanged.
Feature compatibility and security assurance are separate questions. A plug fits the socket; you still need to know what the device does.
Risks and Limits to Check
Module installation grants real authority
Installing a module is not like installing a harmless visual theme. A validator can influence authorization, and an executor can initiate account calls. Verify the module address, type, initialization data, supported chain, audit history, and publisher through independent official sources.
Delegatecall can expose the whole account
The specification warns that delegatecall execution requires special care. Delegatecall runs target code in the account's storage context. Unsafe target code may corrupt ownership, module configuration, or other critical state.
Callbacks and removal can fail
onInstall and onUninstall are external callbacks, so implementations must consider reentrancy. A malicious module may also revert during uninstallation and try to make itself difficult to remove. Builders need defensive removal and recovery design; users need to know the emergency path before depositing meaningful funds.
Hooks can become denial-of-service points
A hook that always reverts can stop executions. A hook that checks only one path may create false confidence while another path bypasses the policy. Review which actions actually invoke a hook, including account-configuration changes.
Registries are signals, not guarantees
Draft ERC-7484 proposes registries and adapters that store and check attestations about modules. An attestation can help an account apply a trust policy, but it shifts attention to the attester, registry rules, revocation speed, and adapter behavior. It is not the same as a guarantee or insurance.
A Practical Module Review Checklist
Before enabling a module on a smart account:
- Confirm the wallet and exact account version support ERC-7579 or a named adapter.
- Verify the module contract address and module type from official documentation.
- Read what authority the module receives, including future or automated actions.
- Check supported execution modes, especially batch and delegatecall behavior.
- Review audits, source-code verification, upgrade controls, and registry attestations.
- Confirm who can change configuration and whether a delay or multisig applies.
- Test installation, normal use, and uninstallation with a low-value account.
- Document an emergency recovery route if the module or hook blocks execution.
- Revoke or uninstall modules that are no longer needed.
Caution
A familiar wallet brand does not automatically validate every third-party module. Treat the module address and requested authority as separate security decisions.
Frequently Asked Questions
Is ERC-7579 live on Ethereum?
It is a draft ERC that projects can implement in contracts and adapters; it is not a network-wide protocol feature automatically enabled for every account. Check the official ERC status and your wallet's current documentation before relying on it.
Is ERC-7579 the same as ERC-4337?
No. ERC-4337 defines an account-abstraction transaction flow around UserOperations, bundlers, and an EntryPoint. ERC-7579 defines minimum interfaces and behavior for modular smart accounts and their modules, and its current validation design depends on ERC-4337.
Does ERC-7579 make modules safe?
No. It can make interfaces interoperable, but module code, initialization, upgrades, authorization, and wallet integration still need review. The official specification includes warnings about delegatecall, callbacks, malicious hooks, fallback authorization, and uninstall failures.
Can one module serve several roles?
Yes. A module can report more than one type. The account must still distinguish those types and enforce the correct authorization for each role.
Can an existing smart account become compliant?
Potentially. The specification notes that upgradeable accounts may adopt a compliant implementation, while some non-upgradeable accounts may use an adapter or fallback mechanism. Feasibility and safety depend on the account's original architecture.
The Practical Takeaway
ERC-7579 is an attempt to give smart-account features a common, minimal connector. Validators decide whether authority is valid, executors initiate actions, fallback handlers extend interfaces, and hooks inspect execution. That separation can improve portability and reduce vendor-specific integrations.
It also makes module review a core wallet-security skill. Before installing anything, verify the exact address and type, understand its maximum authority, examine upgrade and removal controls, and test with limited funds. Interoperability lowers integration friction; it does not remove smart-contract or operational risk.
This article is educational and not financial advice (NFA). Smart-account and module software can fail, and crypto assets may be lost. Do your own research (DYOR) and use only funds you can afford to lose.
Keep learning
Account Abstraction Explained: How Smart Wallets Work (2026)
Learn how account abstraction and ERC-4337 smart wallets work — seedless recovery, gasless transactions, and passkeys. A 2026 guide to smarter crypto wallets.
 GOMTU8 min read
ERC-4337 Paymasters Explained: How Gas Sponsorship Works
Learn how ERC-4337 paymasters sponsor gas, support token fee payments, and introduce security and availability trade-offs for smart-wallet users.
GOMTU6 min read
ERC-1271 Smart Contract Signatures: How Wallets Verify Authority
ERC-1271 lets smart contract wallets validate signatures with programmable rules. Learn how isValidSignature works, where compatibility breaks, and key risks.
GOMTU7 min readExplore related topics
Pending Ethereum Transactions: Diagnose, Speed Up, or Cancel Safely
Learn why an Ethereum transaction stays pending, how nonce order and fees affect it, and when speeding up, canceling, or waiting is the safest response.
GOMTU7 min read
Ethereum Glamsterdam Upgrade: ePBS, BALs, and What Is Actually Planned
Ethereum Glamsterdam reached Sepolia, but its Hoodi activation was postponed. Learn why, what ePBS and BALs change, and what remains uncertain.
GOMTU8 min read